Cybersecurity consultant · Jakarta
Security is a habit, not a gate.
I help teams keep software safe while it keeps moving. Good security is quiet. It lives in how people work, not in a checkpoint at the end.
- 15+years of building and securing software
- 4public talks since 2023
- 2023Best Pre-Sales Consultant in Southeast Asia, OpenText
Who are you?
A developer who became a security consultant, and never forgot the first part. I wrote Oracle modules in 2010, built a registration platform for running events in 2011 that I still run today, and spent most of the years since inside telecoms, ministries and enterprises in Indonesia and Japan, helping them protect what they build.
I live in Jakarta. I work in Indonesian and English. These days I lead the technical side of security sales for Southeast Asia at OpenText, and I take on independent work when the problem is interesting.
What do you believe?
That security is a habit. Four things follow from that.
What would you do for me?
Usually one of four things, and often two of them together. I say early which one you need, and whether you need me at all.
- Make delivery safe
- Security built into the pipeline: threat modelling, code and dependency scanning, secret and policy checks, with a security champion in every team. The industry calls it DevSecOps and application security.
- Protect the data
- Find the sensitive data, sort it, encrypt it, and keep the test copies safe. Mapped to Indonesia's PDP Law and the laws of its neighbours.
- Watch and respond
- Logs, detection and automatic response, so known attacks are seen while they happen. SOC roadmaps for telecoms and enterprises.
- Decide who gets in
- Single sign-on, multi-factor and privileged access, so the right people reach the right systems and nobody else does.
How does it go?
Look first. Then plan. Then change one thing at a time, and keep it. Five verbs, always in this order.
Look
I test what faces the internet, the network inside and the applications, and rank every finding by what it would cost the business.
Compare
I set the current state against frameworks such as OWASP DSOMM, NIST and ISO 27001, so every gap has a name and an owner.
Plan
Work is ordered by risk and dependency into phases. Each phase has a clear exit and numbers to meet.
Change
A control starts in a pilot, then runs on its own, and only then becomes a rule for every release. Teams keep shipping.
Keep
Metrics, audits and regular reviews keep the habit honest after the first wins.
What have you done?
Six stories. Where a client is confidential, the name is left out and the facts stay.
 2025
DevSecOps from zero in twelve months
Four measured phases. Security moved from a manual check before go-live into every commit and every build.
 2026
Security posture programme
Five phases and nine pillars. A programme that shows leadership where to act first, and proves the progress.
 2021 to now
Data protection and PDPA readiness
Each country's rules mapped for PDPA compliance, and a data-centred approach that opened new markets.
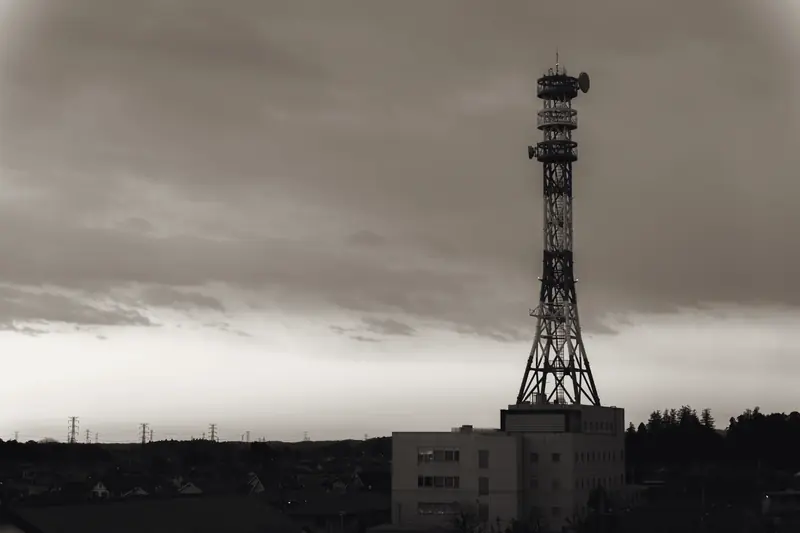 2019 to 2021
Telecom security in Indonesia and Japan
NIST compliance up by more than 30% in six months, a SOC roadmap, and custom tools joined to the SIEM.
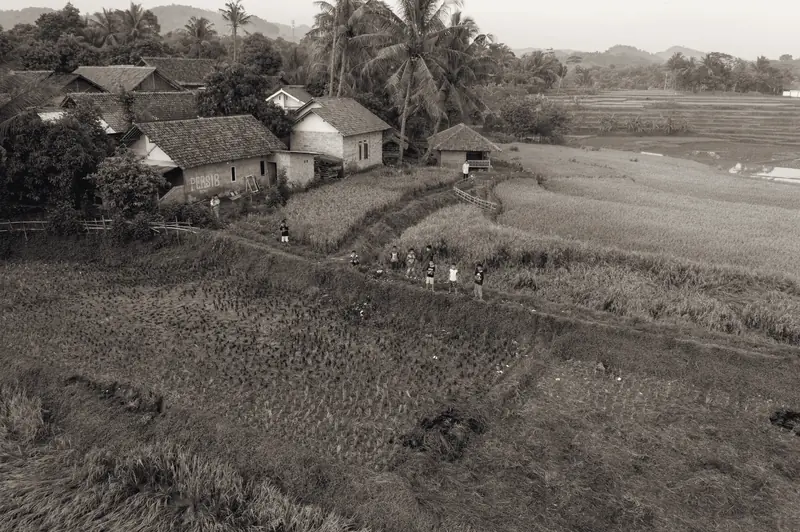 2022 to 2023
Government portal and secure SDLC
A nationwide portal that works on slow connections in remote places, then security built into how the ministry writes software.
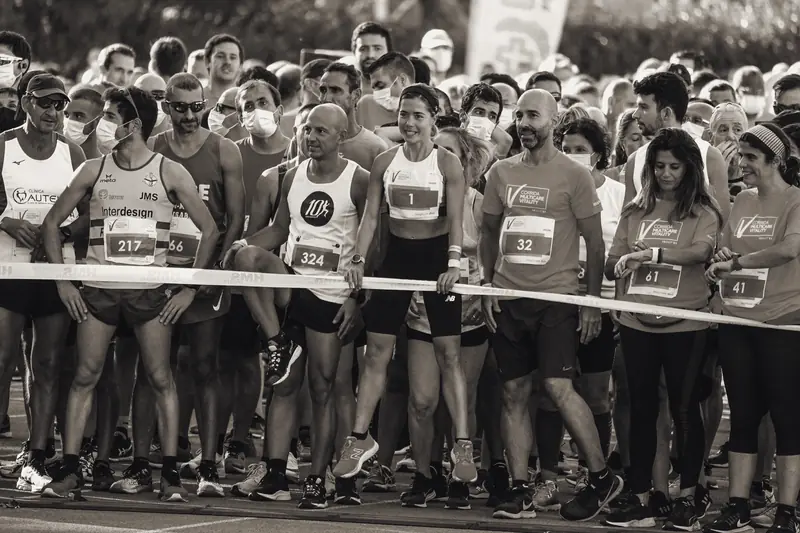 2011 to now
Sports event registration platform
Registration, payments, race packs and timing, built for peaks above a million requests per second.
Where have you spoken?
Four talks since 2023, all on the same idea: security that is built in, not bolted on.
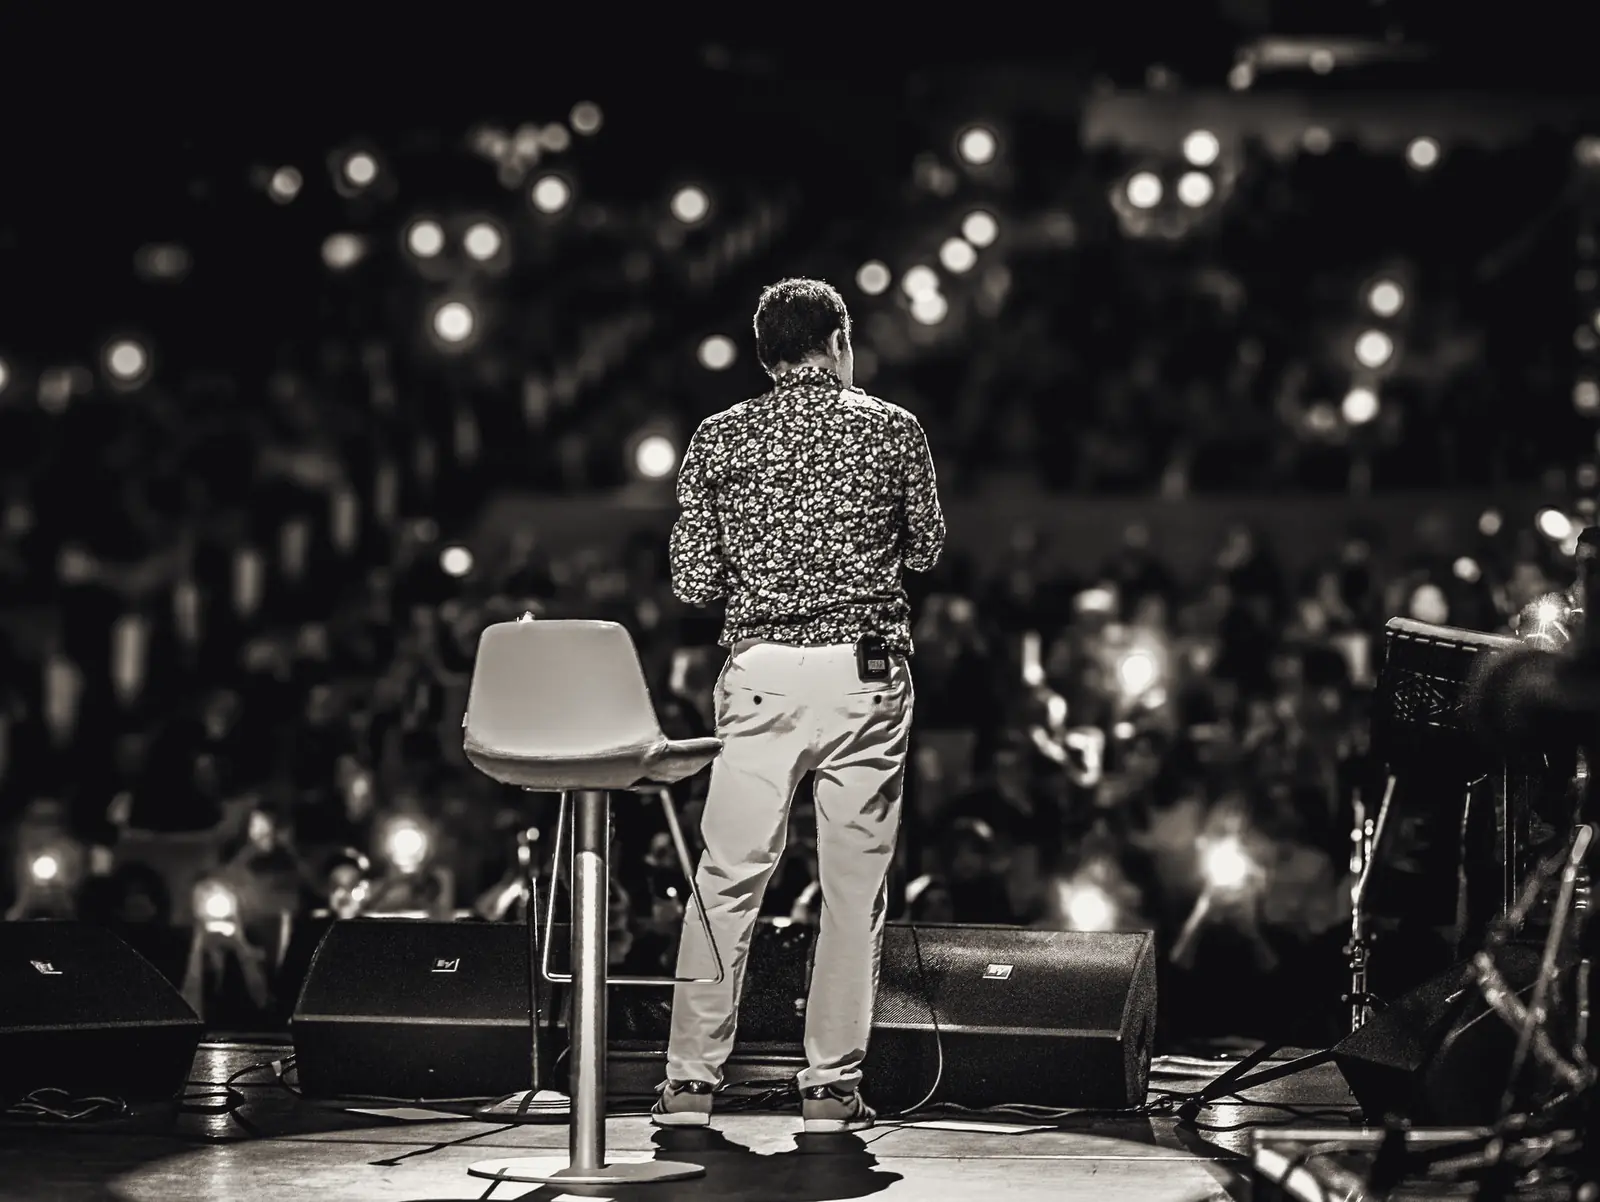
- Hackpoint Community Webinar, online
Securing the Software Development Lifecycle by design
Security as part of how software is made, not a step after it, so risk goes down and delivery stays fast.
- DevOpsDays Jakarta
Securing DevOps: data privacy and protection in continuous deployment
Trust nothing by default. Data is checked and encrypted in transit, in use and at rest, every time.
- Forum Digital BUMN (Fordigi), Jakarta
Embark on a secure and resilient application SDLC
End-to-end application security against attacks on the application layer and on the supply chain.
- Indonesia Data Security Symposium, Jakarta
Pioneering data-centric protection
What Indonesia's PDP Law asks of an organisation, and how modern tools and frameworks help meet it.
How do I reach you?
Write to me. Tell me where things stand and what has to change. I will answer honestly, including when the honest answer is that you do not need me.