What was the question?
What does the law mean for us, exactly? Every country in Southeast Asia now has a data protection law, each with its own duties and its own deadlines. The organisations asking were not careless. They simply held sensitive data in more places than anyone had written down: production databases, test environments, file shares, pipelines. You cannot protect what you cannot find, and you cannot comply with a law you have not translated into your own systems. Compliance starts with an honest map. The same protection follows the data through all three states.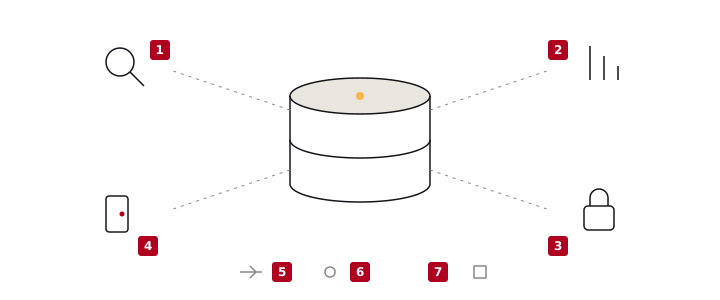
What did I do?
I mapped the rules of each country in the region against what a company actually has to do, system by system. That map did two things at once. It gave customers a path to compliance they could follow, and it opened the way to new markets in Southeast Asia, because the same approach worked across borders.
The approach itself puts the data in the centre and asks four questions in order. Where is the sensitive data? Find it, wherever it sits. How sensitive is it? Sort it. Who could read it if they got in? Encrypt it, in production and in the test copies, where it is usually forgotten, with test data management. Who may reach it at all? Control that, and keep controlling it. The same protection follows the data through its whole life: in transit, in use and at rest.
I said all this in public too, at the Indonesia Data Security Symposium in 2023 and at DevOpsDays Jakarta in 2024, on zero-trust data protection in continuous deployment. And I joined it to delivery: an operational DevSecOps framework across customers’ business units, so data protection and application security happen in the same process rather than in two meetings.
What came of it?
The team became the market leader for data security coverage in Indonesia. Customer retention in Indonesia reached the highest rate in the region. The work was part of the Indonesian cybersecurity sales team’s President’s Club recognition, year after year. In 2023 I was named Best South East Asia Pre-Sales Consultant. The part I am proudest of is quieter: companies that now know where their data is.