An application is rarely written by one team alone. Most of its code is borrowed: open-source libraries, frameworks, components from vendors, services it calls. Protecting the application therefore means protecting the whole of it, the parts written in-house and the parts that came from elsewhere, and knowing at any moment what those parts are. Resilience follows. When a weakness is found in a borrowed part, the team that knows where it is used can act in hours.
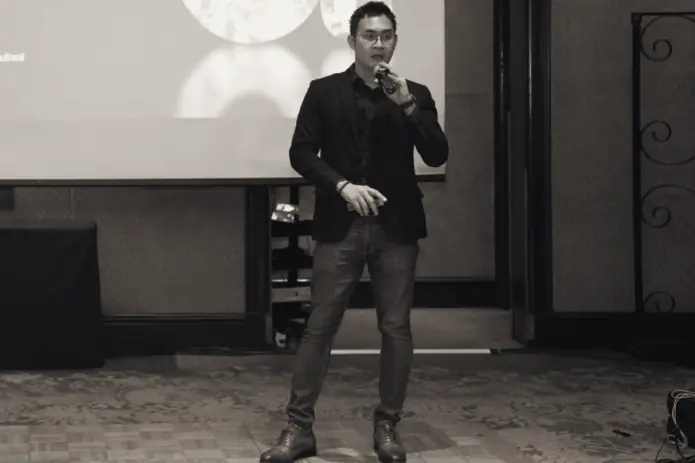
I gave this talk at Forum Digital BUMN (Fordigi) in Jakarta in February 2024.